Software Project Rescue: All Websites Back Up and Running, Business Saved (2026)
Summary
The client’s websites were down almost all the time. The previous provider did a bad job. The client hired Belitsoft to take over the web application and make it stable. Belitsoft’s DevOps engineers and developers rescued the cloud server and the web application and got all the client’s web services back online. Today, this network of websites is running properly, and the client has stopped worrying and is comfortable sleeping at night.
Client
The client is a digital media company based in Victoria, London, United Kingdom, with 20+ employees. Its proprietary B2B database platform, a .NET-based web application, has been developed over 15+ years. The platform runs the client's network of websites and is its lead generation machine. The company's audience fill out a form with their business details to access gated content on the document management platform. Every new lead goes into the CRM.
Challenge
Business on the line
It happened on a Sunday at the beginning of a month. Bots went through the catalogue pages of the platform non-stop, and the sites started going down.
The server was overloaded and the sites had major page loading issues.
The client's business lives and dies by the leads coming through the sites, so when the sites went down, the whole business was on the line.
The previous provider did a bad job
Cloudflare was no longer working for the client: it blocked the bots at the front door, but the bots found a way around it and reached the server directly.
Akamai promised a more sophisticated solution, so the client switched over.
Akamai Security was installed and initially configured by the BV TECH Group, a previous third-party provider servicing the market as an Akamai partner. When the bots came and the sites started going down, they were managing the configuration.
Big promises, poor results
The client expected a boxed solution for the bot problem. With these tools everyone promises out-of-the-box protection. However, the client was not happy: it did not get the expected results.
What the BV TECH Group did about the bots failed to remedy the situation.
Moreover, their last change locked legitimate users out along with the bots.
The BV TECH Group did the bare minimum and wouldn't go out of the way to fix anything if it wasn't explicit in the scope.
Misunderstood the application
The previous contractor knew the Akamai product, but could not make sense of the client's application. The advice was of the generic kind.
Looking for a fresh set of eyes and hands
The client was looking for someone to come in and give an independent assessment, a fresh set of eyes and hands. Our client needed a development partner with significant web and application development expertise, who could get under the bonnet of the application, not just an Akamai consultancy and implementation services.
Solution
Rescue Audit
01 Understanding the Client's Project
Belitsoft stepped in, took the Akamai configuration into its own hands and started making the changes itself. Initially, Belitsoft had to review, audit and understand the current system. It started with a detailed audit of the existing setup. Belitsoft went through the settings line by line to understand how the application worked: which URLs exist and which don't, how many pages a site visitor opens in a minute, how often an actual customer submits a form, and where the client's audience comes from. The Akamai rules were built on that understanding.
02 Akamai Configuration Review
Then Belitsoft's engineer went through everything with a fine-tooth comb to understand what the previous provider had done wrong, noting what worked and what didn't, and made a list of things the old vendor had done incorrectly or left unfinished. For example, Origin Health Detection, enabled on the provider's advice, had produced no noticeable result. Blocking individual IP addresses hadn't worked either. The TLS fingerprint rule, that vendor's last change, had locked legitimate users out along with the bots.
Rescue Planning
03 Decision on What to Keep, Switch Off or Add
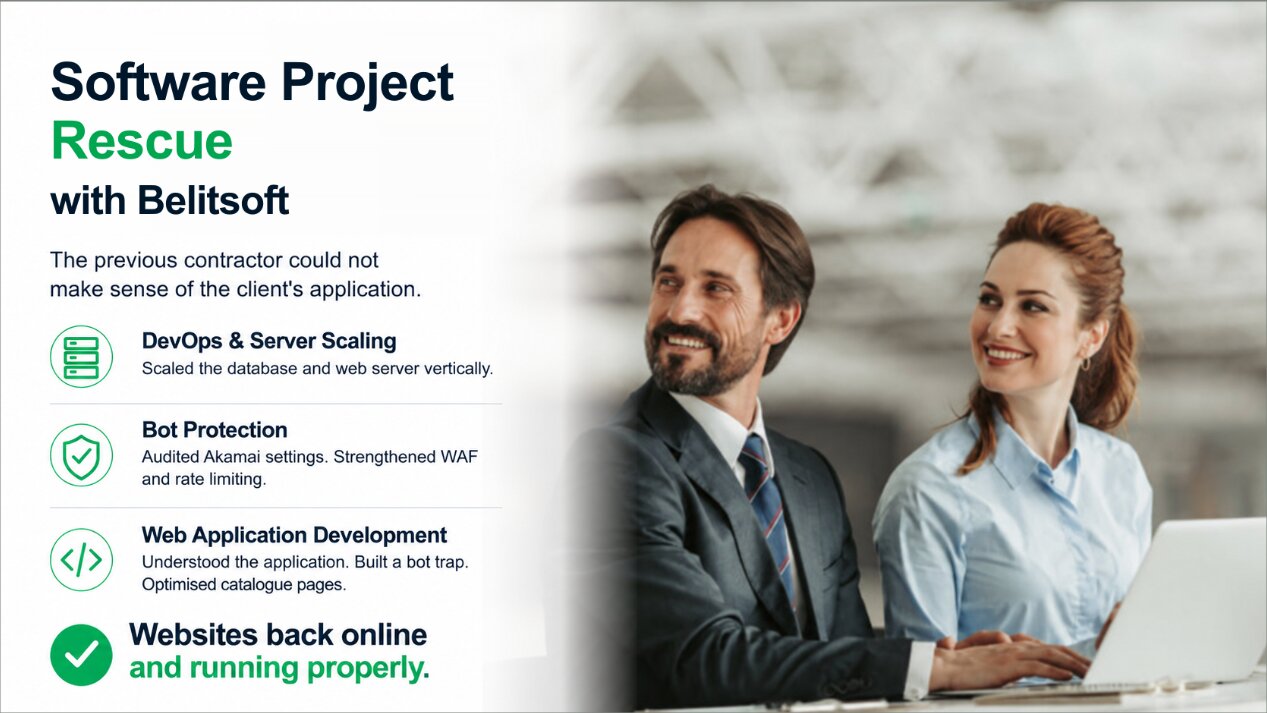
Based on that list, Belitsoft went through an inventory process, determining which settings to keep, which to jettison and what to add. The blocking of whole subnets was jettisoned. Blocking whole countries, rate limiting, the WAF rules, stronger known-bot blocking and Akamai's Content Protector module were added. The server was to be scaled up, and the application was to get a bot trap.
04 Prioritisation & Project Planning
Akamai did the bulk of the work. However, the work went beyond simply setting up Akamai. Both a boxed solution like Akamai and the application have to be properly configured and tuned.
05 Project Resource Allocation
Belitsoft's DevOps engineers worked on the server side and Belitsoft's developers on the application side.
Software Project Rescue
Geo blocking. Blocking whole subnets of one region did work. However, the client had real users in that region too, so Belitsoft blocked the countries with the largest share of malicious traffic instead, which reduced all traffic by 31%.
Rate limiting. This was the biggest win. Belitsoft put its foot down and insisted on implementing it and fine-tuning it further. In one month the rate limiting rules blocked 10.4M requests. Half of them came from a 'fail to ban' rule for bots that keep coming back for non-existent pages. Another 4.6M came from bots that open the same pages far more often than the regular audience would, 0.3M from bots that submit forms too often, and the rest from rules on the key pages.
Rules specific to the application. On top of that, Belitsoft added rules that come from knowing exactly what the application does. A block on query string parameters the application never uses removed 1.1M bot requests a month. A blacklist of paths that don't exist, with a whitelist of the ones that do, removed another 0.7M.
Known bots. Known-bot blocking was beefed up to 1.0M requests a month, and the performance drops from crawlers like SEOKicks completely disappeared.
WAF. Rules that had been switched off were turned back on.
Content Protector. For bots that go through the sites the way actual customers do, Akamai suggested its Content Protector module. The client bought it, and it blocks another 0.9M requests a month.
Cloud server. Belitsoft's DevOps engineers upped the cloud server capacity. Scaling the database and web server vertically removed the overload and increased the stability of the environment.
Web application. The developers built a bot trap and optimised the catalogue pages the bots go through most.
Results & Feedback
Back online and running properly
The main result is that the network of the client's websites is back online and running properly. Now, as the client put it at a recent meeting, 'at the moment, fingers crossed, it's not disrupting business, as before it was'.
Server rescued, stable work restored
Belitsoft rescued the server and fixed the root issue. Before the incident, it failed to serve only 3% of requests, which most users never noticed. After a month of bot scrapers going through the sites, this figure went up to the point where pages didn't open at all. After Belitsoft's work it went down to 2% and less, which is in fact better than before the attack.
Bots blocked before they ever hit the server
The bots did not go away. They still come, but in one of the recent months 31.8M requests came to Akamai and 20.7M of them, two out of three, were blocked before they ever hit the server. That means much less stress on the server and no errors or downtime caused by bots.
Business saved
The client can now focus on the business instead of fighting bots. It has stopped worrying and is comfortable sleeping at night.
One phone call away
This was a one-off rescue project, and it's finished, but Belitsoft remains on standby to put out any 'fires' before they can grow and provide backup support.
Bots get smarter year by year, and the settings that work today may not be so effective over time. That's why tools like Akamai keep adding new configurations and tools to block them, which naturally means additional configuration overhead. However, so far the client has had no reason to reach out.